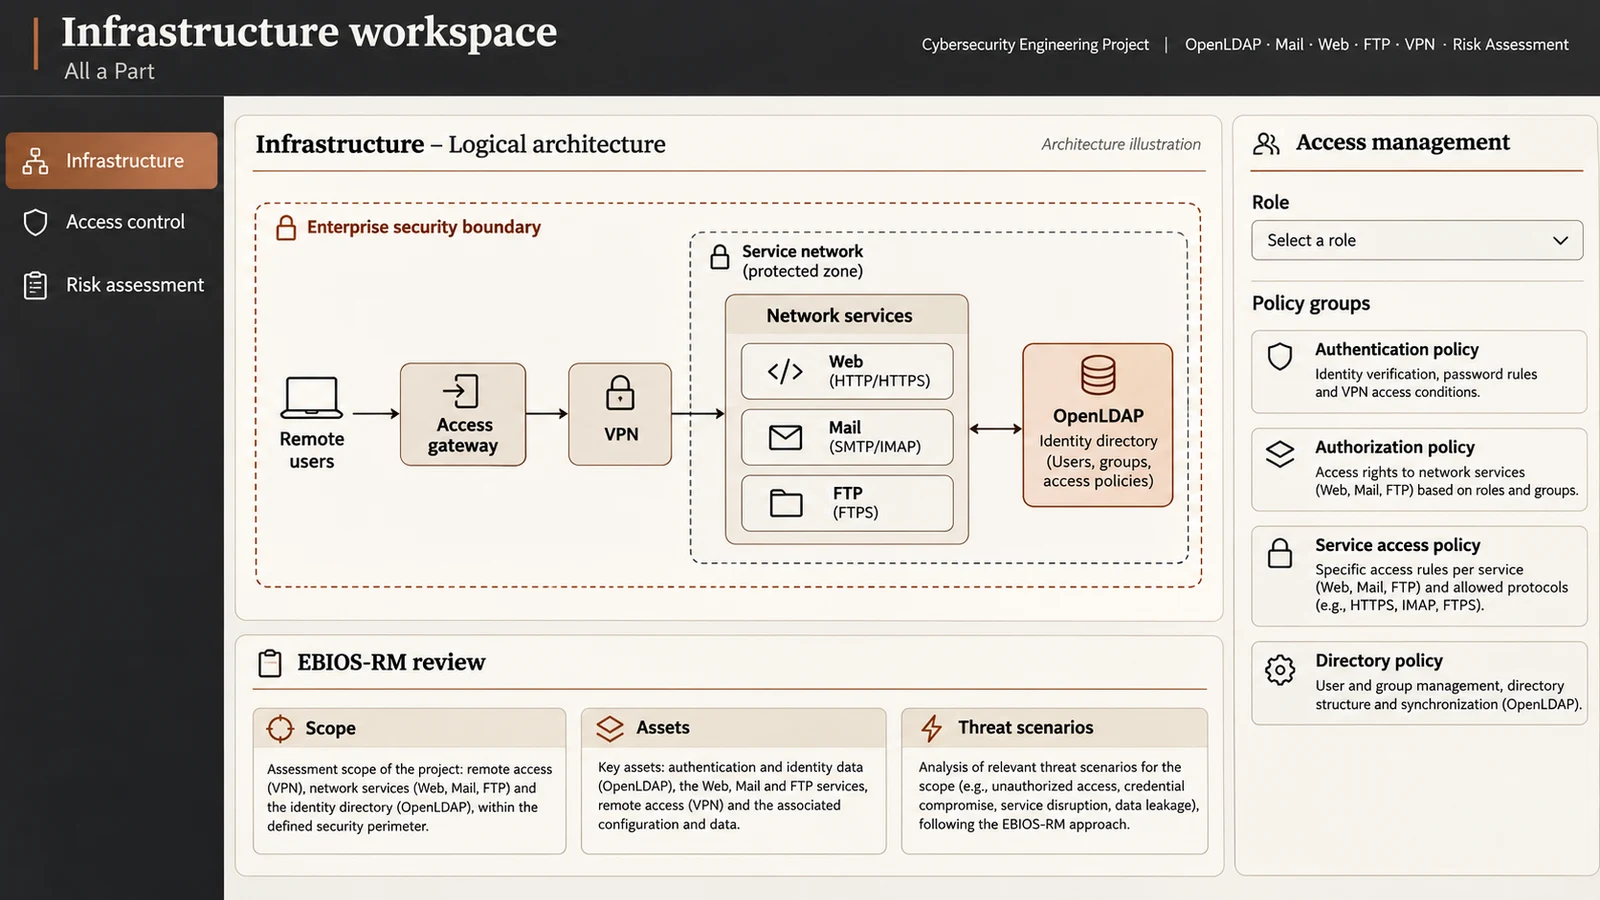
 Interface illustration
All a Part
A secure information system bringing identity, network services, access management, and risk assessment together.
OpenLDAPVPNWeb / Mail / FTPEBIOS-RM
I investigate vulnerabilities,
test security in practice,
and share what I learn.
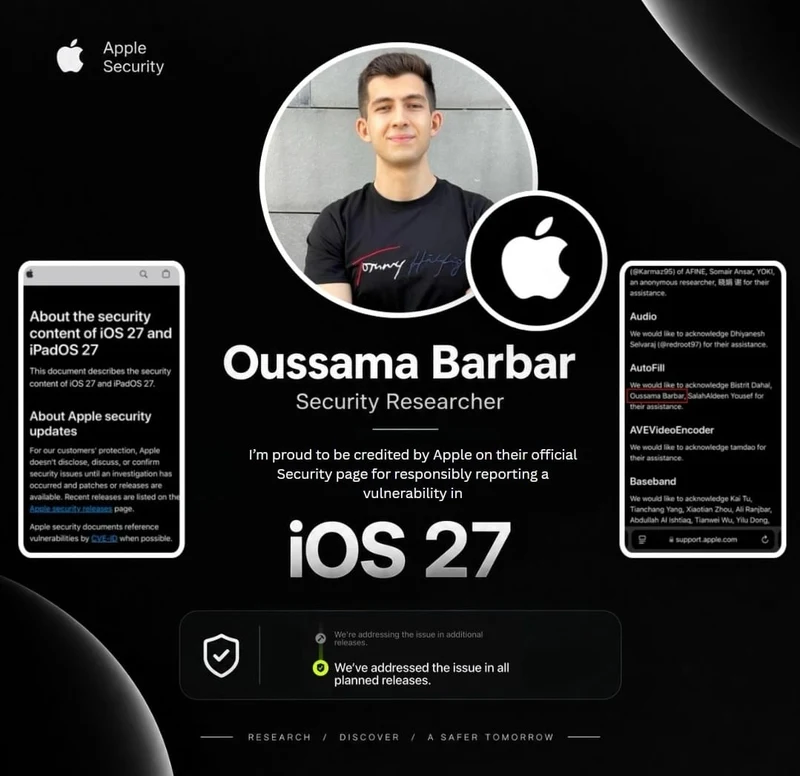
Responsible disclosure / 2026
My name appears in Apple’s official security acknowledgements for iOS 27 and iPadOS 27, following a responsible vulnerability report.
The acknowledgement is listed under AutoFill in the page’s Additional recognition section.
View Apple acknowledgementIndependent security research and responsible disclosure.
Research, tools & practical security
Security engineering projects,
research, and hands-on education.
Interface illustrationA secure information system bringing identity, network services, access management, and risk assessment together.
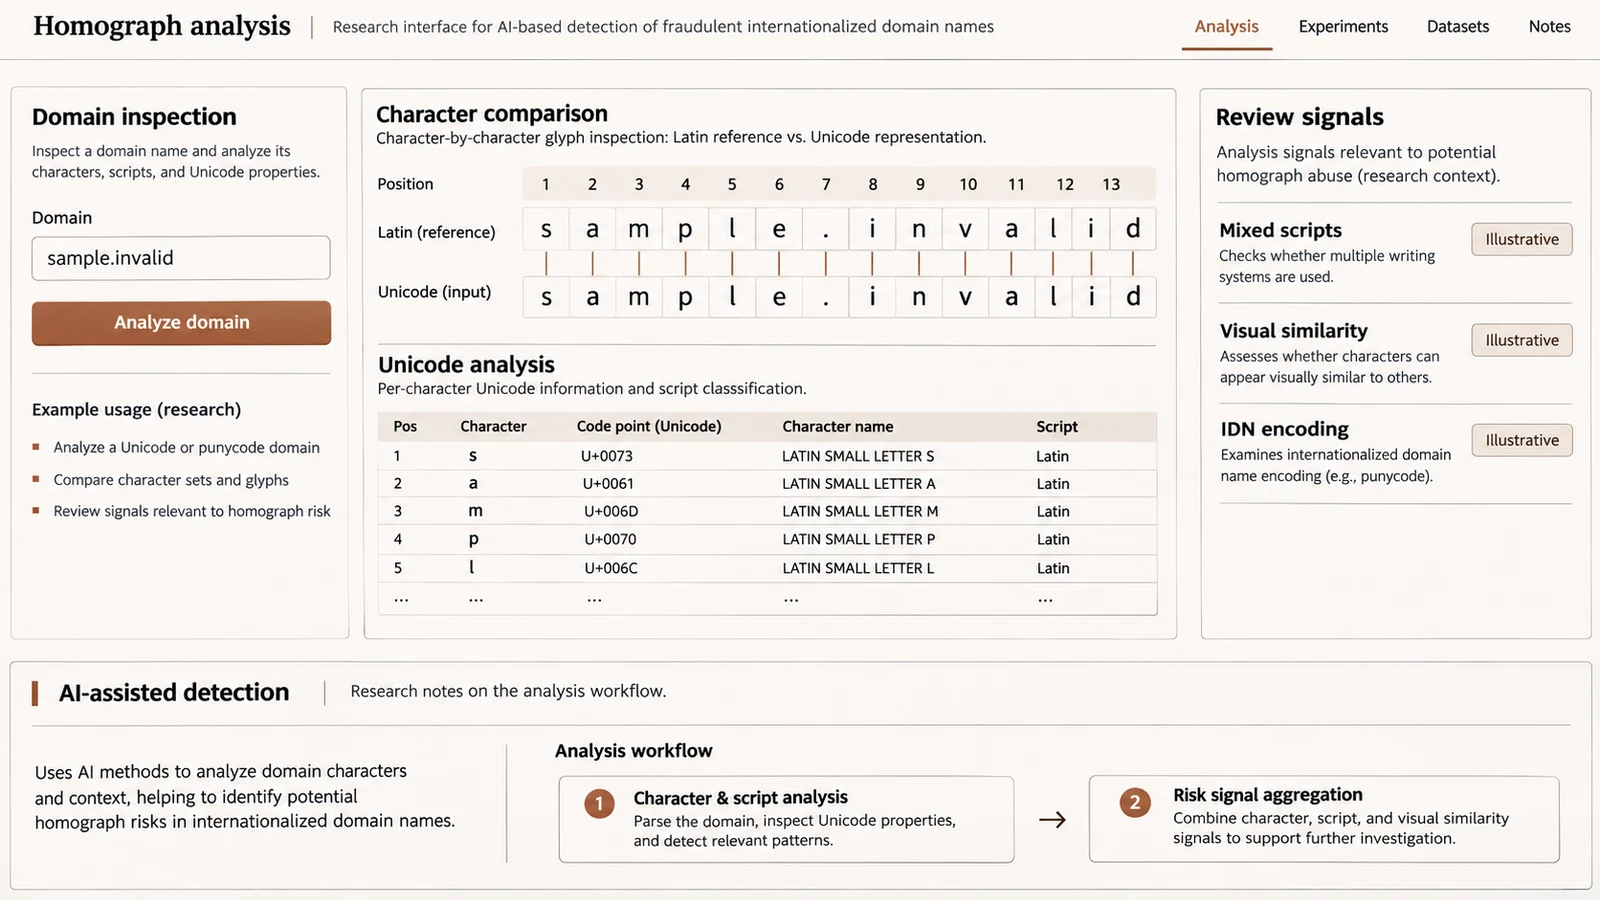 Interface illustration
Research into AI-based detection of fraudulent internationalized domain names used in homograph attacks.
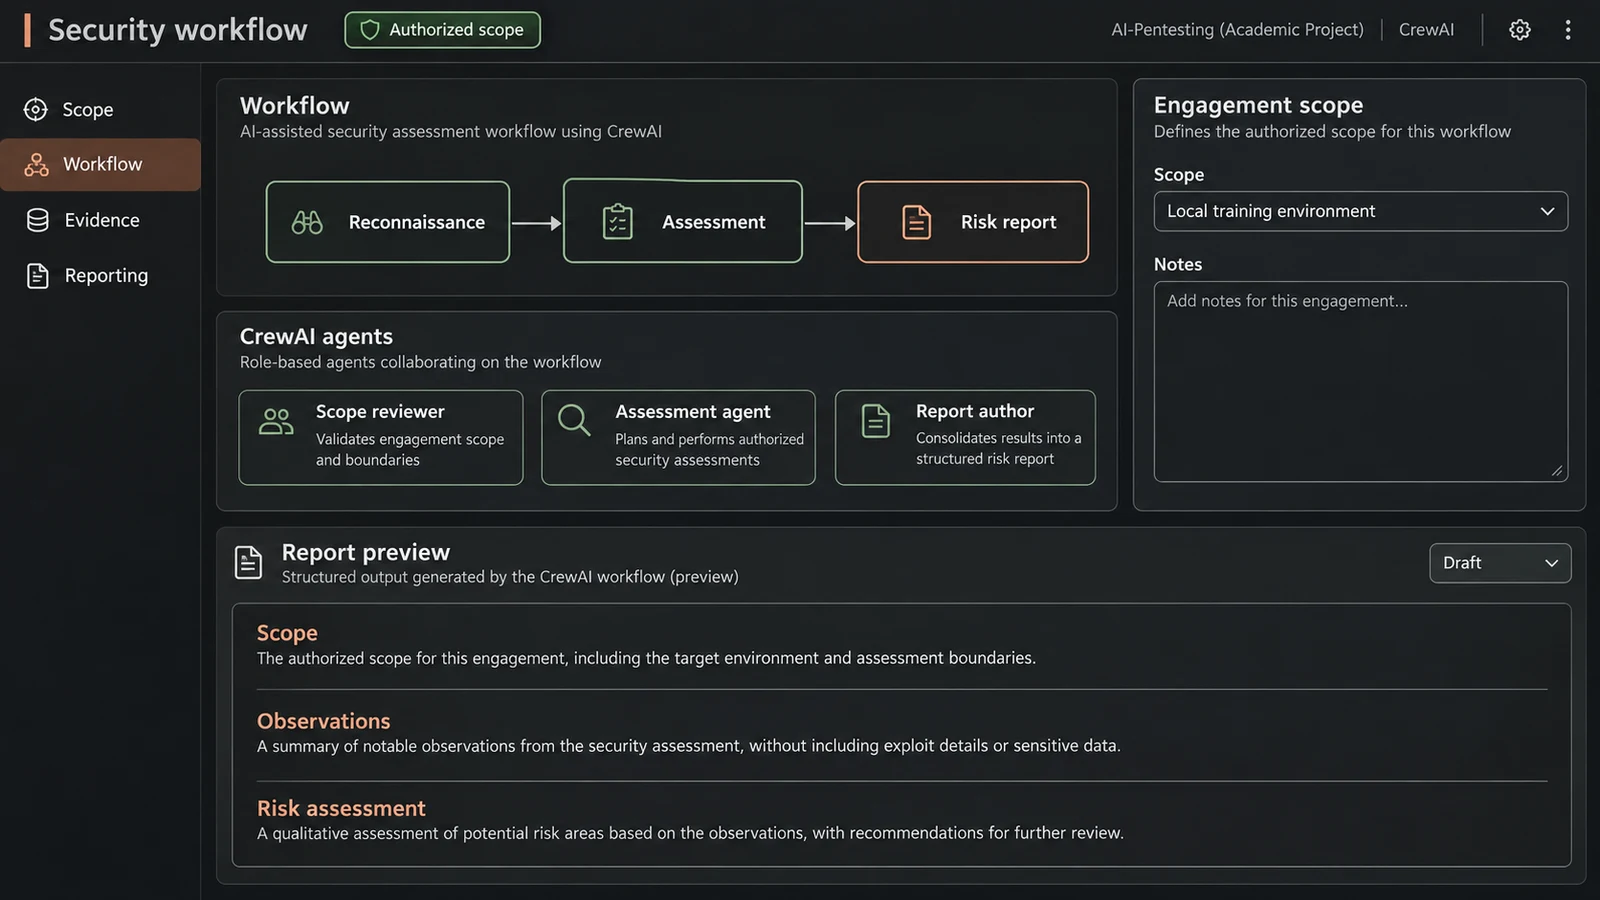 Interface illustration
An automated penetration-testing workflow using CrewAI, spanning reconnaissance, assessment, and risk reporting.
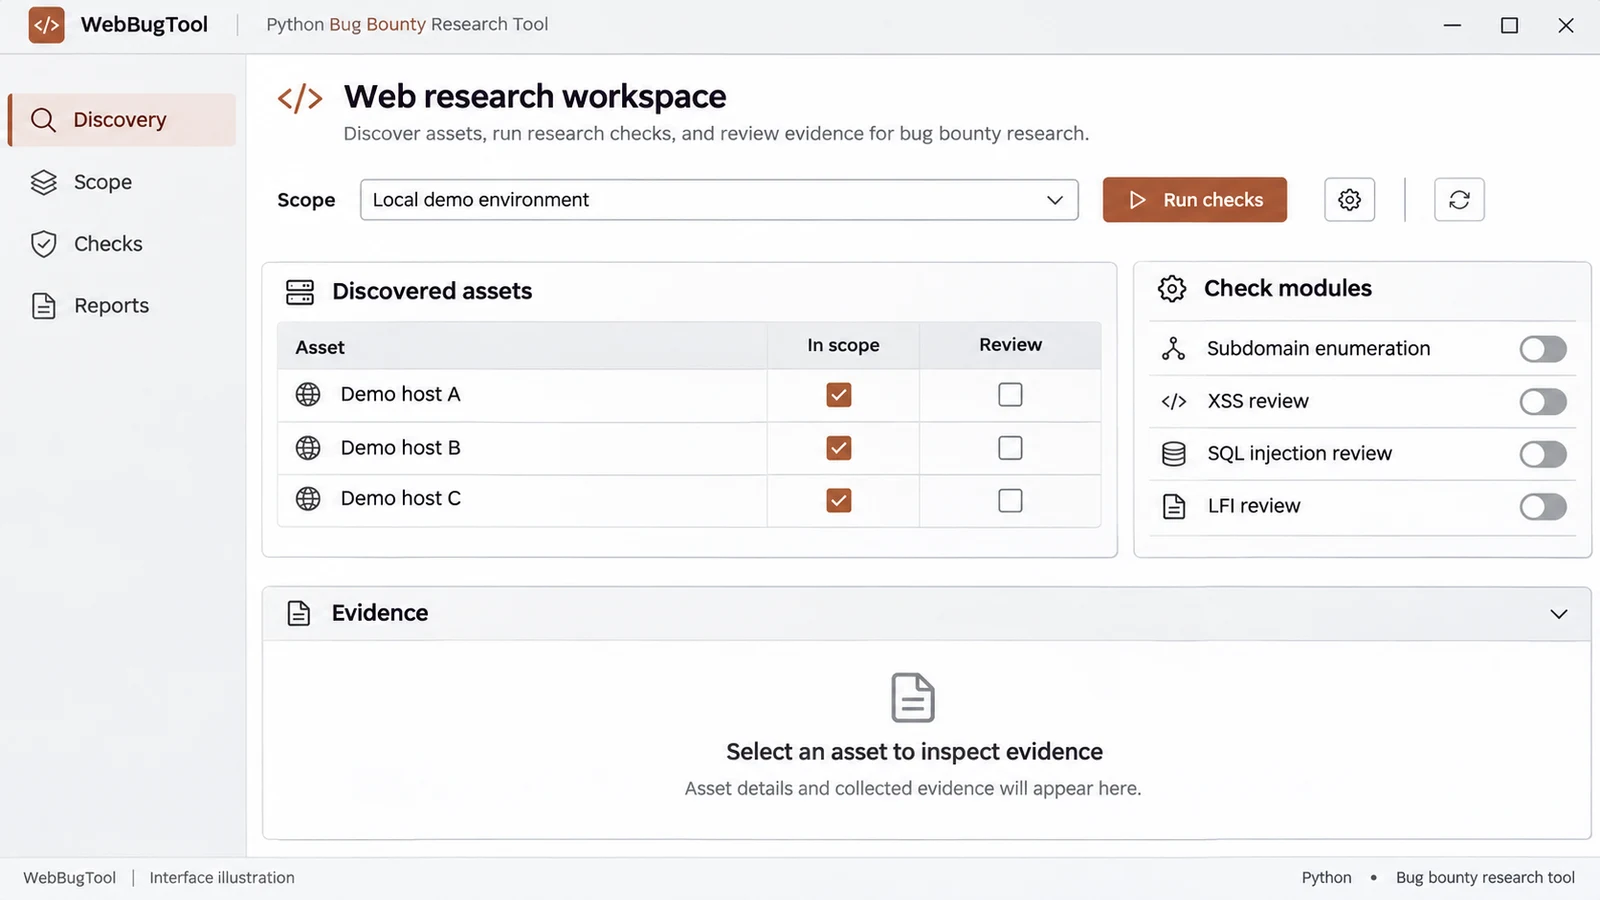 Interface illustration
A Python research tool for discovering subdomains and reviewing common web-application vulnerabilities.
A cybersecurity and ethical hacking training platform with hands-on paths in penetration testing and bug bounty hunting.
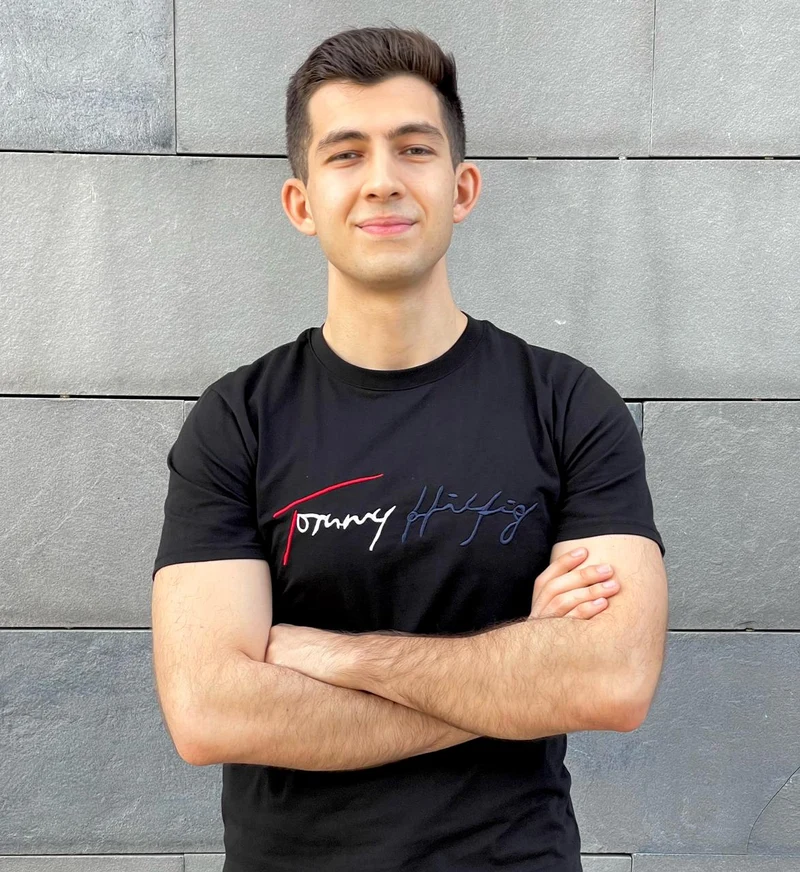
The researcher behind the work
I’m a cybersecurity engineer focused on penetration testing, offensive security, and security consulting. My engineering background spans Télécom Paris and the Lebanese University.
I work across hands-on assessment and governance: investigating web vulnerabilities, preparing technical reports, and contributing to compliance and risk engagements.
Through FoxVoid Academy, I turn practical security knowledge into training and learning paths for penetration testing and bug bounty hunting.
Assessment, disclosure & security education
From network operations
to research and consulting.
Created a cybersecurity and ethical hacking training platform with hands-on learning paths in penetration testing and bug bounty hunting.
Identified and responsibly disclosed web vulnerabilities affecting organizations including Yahoo, TeamViewer, and Withings through platforms such as YesWeHack and HackerOne. Prepared impact assessments and technical reports, with ongoing research into Android application security.
Contributed to GRC and regulatory compliance engagements involving DORA and ISO 27001. Participated in Red Team exercises, Wi-Fi security audits, web penetration tests, and vulnerability assessments.
Contributed to network operations involving switching, access networks, and data and voice transmission.
A practical security toolkit
Understanding the risk.
Communicating the findings.
Penetration testingRed TeamWeb securityWi-Fi security auditsBug bounty
Vulnerability assessmentImpact analysisTechnical reportingAndroid application security
DORAISO 27001GRCEBIOS-RM
PythonCrewAIOpenLDAPVPNWeb / Mail / FTP
Cybersecurity instructionHands-on learningArabic · NativeFrench · FluentEnglish · Fluent
Education & professional development
Télécom Paris
Lebanese University · Faculty of Engineering (ULFG1)
TryHackMe · Simulated cybersecurity environments
Semicolon Academy
Invited to MTV Lebanon to discuss cybersecurity and bug bounty research. Recognized in organizational Halls of Fame for responsible disclosures.
Have an opportunity or a question?
Penetration testing, security research,
consulting, and hands-on education.